ai The Next Leap in Application Security: How AI is Moving WAFs from Anomaly Detection to Proactive Threat Verification For years, the Web Application Firewall (WAF) has been the digital bouncer
The Kernel’s Superpower: Why eBPF is the Future of WAF Performance and Observability For years, Web Application Firewalls (WAFs) have been a critical component of
devops The Self-Healing Perimeter The Self-Healing Perimeter: Automating Security Remediation in Modern Pipelines In the
ci/cd Beyond the Handshake Beyond the Handshake: Securing Full-Stack Architectures with Context-Aware WAF Automation
WAF The Adaptive Shield The Adaptive Shield: Automating WAF Rule Updates in DevSecOps As modern application
development Shifting Left: Implementing Security-as-Code Shifting Left: Implementing Security-as-Code to Protect the Modern Application Lifecycle
security Integrating Security Gates The Automated Fortress: Integrating Security Gates into Your CI/CD Pipeline In
DDoS Securing the Modern Stack Securing the Modern Stack: Advanced WAF Strategies and Backend Hardening In an
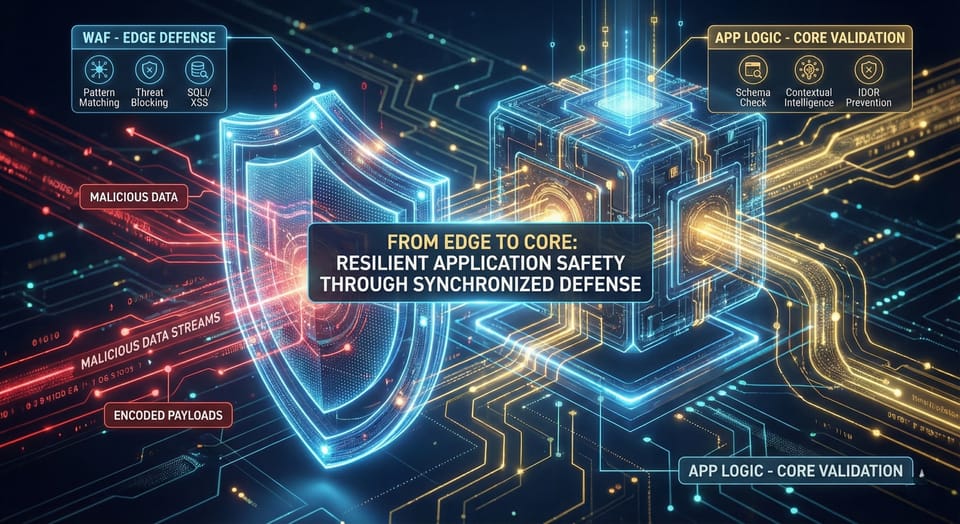
development Building Resilient Application Safety In the modern landscape of cyber security, the boundary between the network
ci Bridging the Gap Between DevOps and Application Security WAF-as-Code: Bridging the Gap Between DevOps and Application Security In
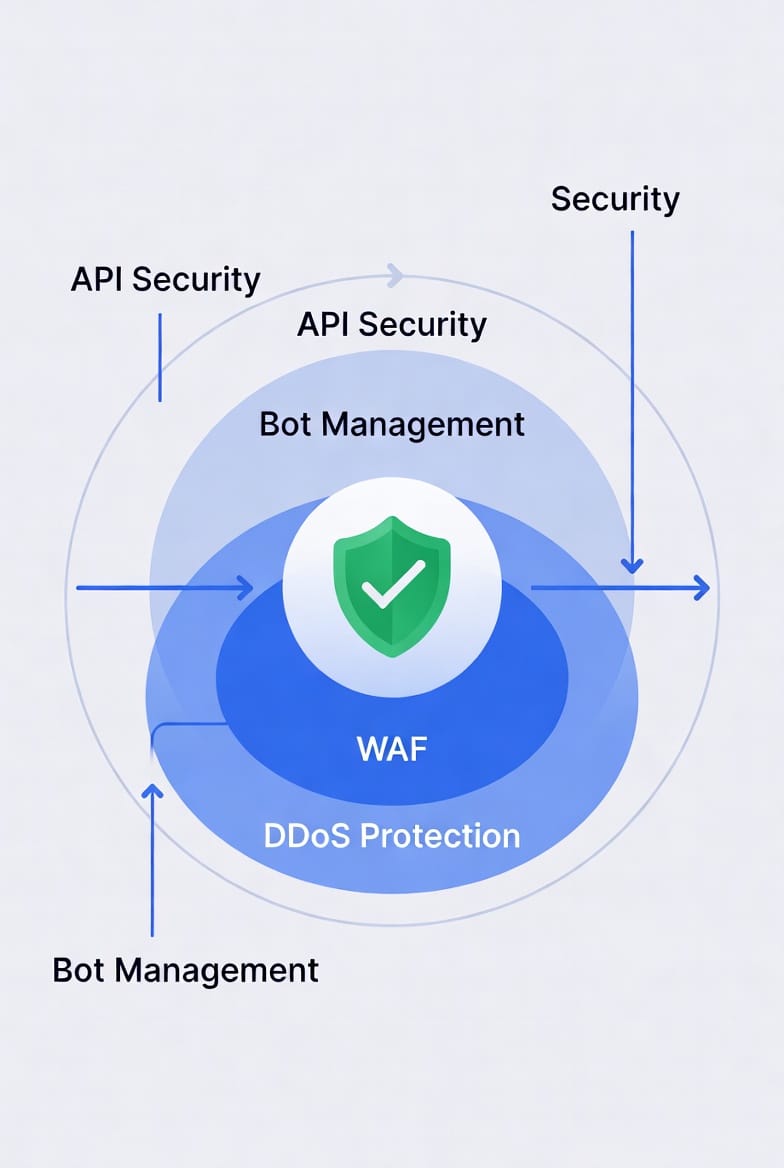
api Defending the Perimeter: Strategic WAF Implementation for Modern Application Security Defending the Perimeter: Strategic WAF Implementation for Modern Application Security In an
WAF The Zero-Trust Pipeline The Zero-Trust Pipeline: Why Application Safety Must Be Decoupled from Infrastructure